Win customer trust and prove your security maturity with Compliance Provider. Our automation-led platform reduces the effort required for ISO 27001 compliance by over 80%, saving more than 200 hours while always keeping you audit-ready.
Trusted by Hundreds of companies and leading innovators
A Smarter Way to Build and Maintain Your ISMS
Compliance Provider removes manual work from ISO 27001 by automating the majority of ISMS activities and guiding you through the remainder. Evidence, risks, training, corrective actions, and monitoring are all managed in one place, without spreadsheets or fragmented tools.
Built for Ongoing Compliance, Not One-Off Certification
Automation First
Generate and maintain policies, controls, and evidence automatically covering over 80% of ISO 27001 requirements.
Always Audit-Ready
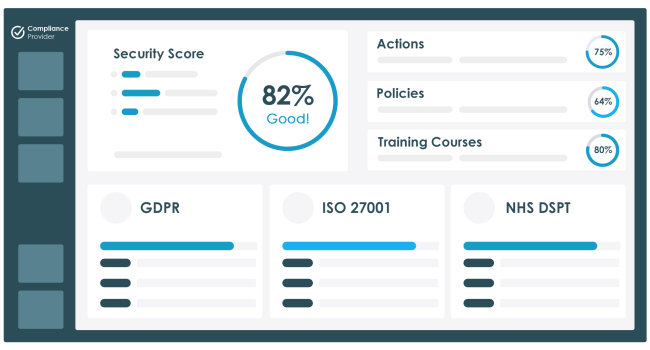
Continuously identify risks, track vulnerabilities, and log compliance activity so your ISMS stays current between audits.
Always Audit-Ready
Continuously identify risks, track vulnerabilities, and log compliance activity so your ISMS stays current between audits.
Human Expertise Included
Access experienced security professionals when judgement, interpretation, or assurance is required, not just software prompts.
Human Expertise Included
Access experienced security professionals when judgement, interpretation, or assurance is required, not just software prompts.
One System, Full Coverage
Manage risks, assets, training, and evidence from a single platform designed specifically for security and compliance teams.
Reduce Time, Cost, and Operational Drag
ISO 27001 often fails due to operational overhead. Compliance Provider eliminates unnecessary effort by automating repeatable work and centralising everything needed to run your ISMS, allowing teams to focus on security outcomes, not administration.
Automation alone is not enough. Compliance Provider’s CISSP and ISO 27001-certified specialists support you through scoping, risk treatment, control selection, and audit preparation, helping you move forward with confidence.
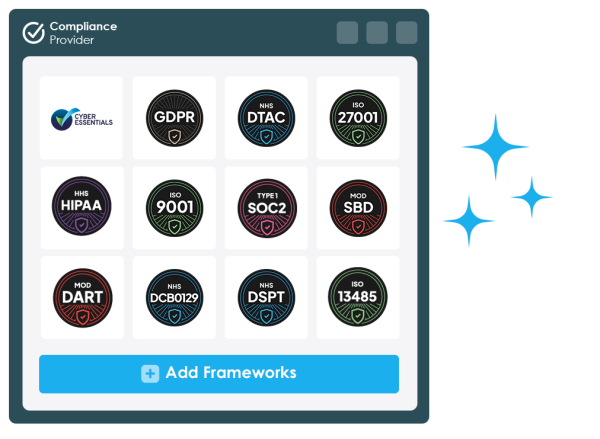
As your compliance landscape grows, Compliance Provider prevents duplication by mapping controls across GDPR, Cyber Essentials, DTAC, ISO 13485, ISO 9001, SOC 2, and HIPAA, reducing workload as new standards are added.